
Progress Orders ShareFile Storage Zone Controllers Offline Over Undisclosed Threat
Summary
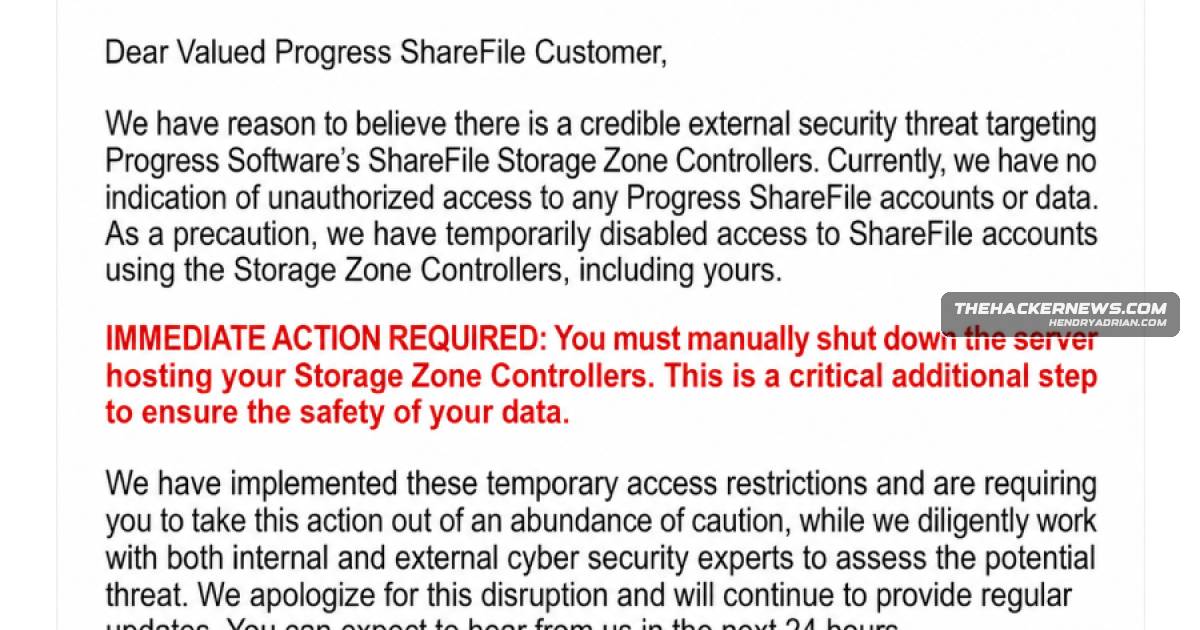
Progress ordered customers to take self-hosted ShareFile Storage Zone Controllers offline over a credible but undisclosed threat. It reported no evidence of account or data access and advised customers to preserve logs and inspect for suspicious .aspx files.
Key points
- Progress said it detected a credible external security threat and instructed customers to shut down Windows servers running self-hosted Storage Zone Controllers.
- The company temporarily disabled affected accounts as a precaution; it reported no indication that ShareFile accounts or data were accessed.
- Progress has not disclosed the threat's nature, who may be responsible, or when customers can safely bring controllers back online.
- Cloud-only ShareFile accounts are not affected, according to the article.
- Progress advised customers to keep controllers offline, preserve logs, begin incident-response procedures, and check for unfamiliar .aspx files.
- The article says versions 5.12.4 or later on the 5.x line, or a 6.x release, address earlier flaws, but Progress has not said those versions resolve the current threat.
- The article notes that CVE-2023-24489 was exploited in 2023; it does not report that the current threat is related to that flaw or to two other flaws disclosed in April.
Article Details
- Event Type
- Progress Software issued an emergency shutdown order after detecting a credible external security threat affecting self-hosted ShareFile Storage Zone Controllers.
- Impact
- Progress temporarily disabled affected accounts and instructed customers to take the controllers offline. It reported no indication of unauthorized access to ShareFile accounts or data, but has not disclosed the threat’s nature or source. Cloud-only ShareFile accounts are not affected.
CVE
Threat Actors
Vendors
CitrixIn 2023, while the product still belonged to Citrix, attackers exploited an unauthenticated flaw in the same Storage Zones Controller (CVE-2023-24489).Progress SoftwareProgress Software has told ShareFile customers to shut down Windows servers running Storage Zone Controllers after detecting a credible external security threat.
Products
Progress MOVEit TransferProgress, which acquired ShareFile in 2024, had already weathered a mass file-transfer attack of its own: MOVEit, whose 2023 zero-day was exploited by the Clop group and hit more than 2,700 organizations.ShareFileProgress Software has told ShareFile customers to shut down Windows servers running Storage Zone Controllers after detecting a credible external security threat.ShareFile Storage Zone ControllerProgress confirmed the disruption on its status page, listing Storage Zone Controller customers as “not operational” and the incident as under investigation as of a 12:12 p.m.