
AWS Network Firewall Adds Route 53 Resolved IP Validation
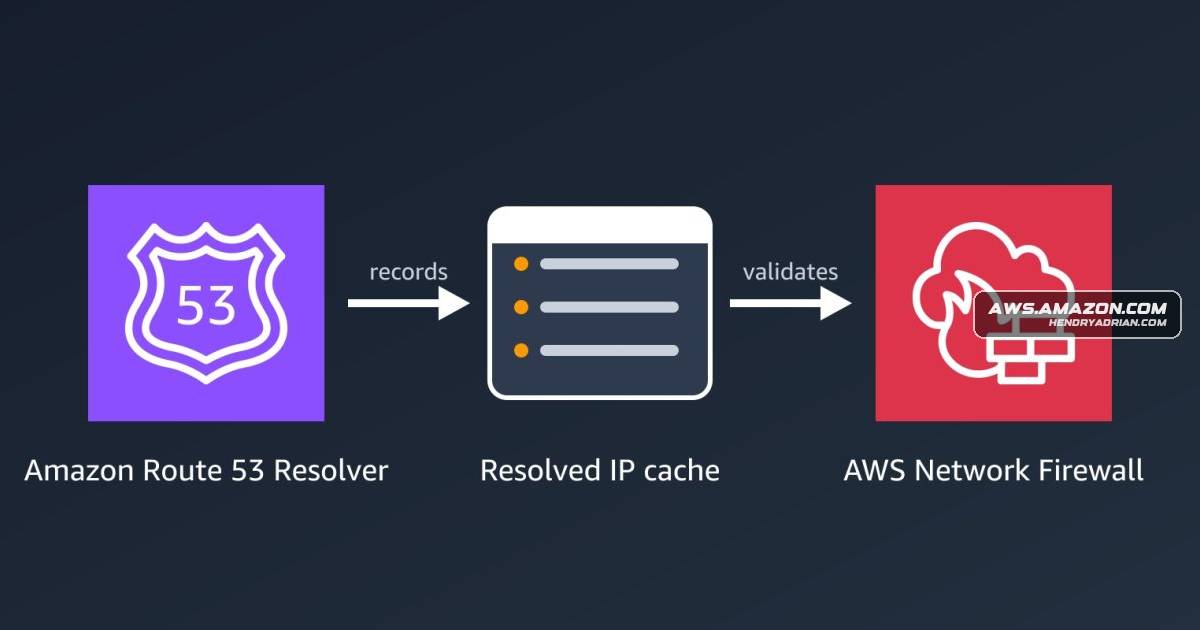
Summary
AWS launched Route 53 Resolved IP Validation for Network Firewall, which checks outbound destinations against Route 53 Resolver answers to enable domain-based controls for non-web traffic and block SNI spoofing without TLS inspection.
Key points
- Launched October 21, 2026, at no additional charge in commercial AWS Regions where Network Firewall and Route 53 Resolver DNS Firewall are available.
- Route 53 Resolver shares returned IP addresses with Network Firewall, which checks each new outbound connection before stateful rules run; the policy can alert, drop, or reject connections that fail validation.
- Resolved-domain stateful rules allow filtering SFTP, SSH, MySQL, and other non-web traffic by domain name instead of maintaining changing IP addresses.
- For TLS, the feature can block connections whose destination IP was not returned for an allowed domain without decrypting traffic; an exact SNI match can additionally check the requested name.
- AWS recommends starting in alert mode, reviewing flow logs and the DnsUnresolvedFlows metric, and allowing about 24 hours for client DNS caches to refresh before enforcement.
- Hardcoded-IP destinations need bypass ranges, and clients using external DNS can bypass the check; AWS recommends keeping DNS on Route 53 Resolver.
Article Details
- Event Type
- Product feature launch
- Impact
- AWS launched Route 53 Resolved IP Validation for AWS Network Firewall at no additional charge. It lets the firewall check outbound connection destinations against IP addresses returned by Route 53 Resolver, enabling domain-based filtering for non-web traffic and helping prevent SNI spoofing without TLS inspection. The feature is available in commercial AWS Regions where the required services are available, excluding AWS GovCloud (US) and China Regions.
Vendors
Products
Amazon Route 53 ResolverAmazon Route 53 Resolver now shares the IP addresses that it returns for each domain name with Network Firewall, and Network Firewall checks each new outbound connection against them.Amazon Route 53 Resolver DNS FirewallAn Amazon Route 53 Resolver DNS Firewall rule group – It defines the scope.AWS Network FirewallFor HTTP and HTTPS, AWS Network Firewall domain rules match the name that the client puts in the request, and the client chooses that name.