
A Go Race Condition Enables File Reads in a CTF Challenge
· 15:08 · Watch on YouTube ↗
Summary
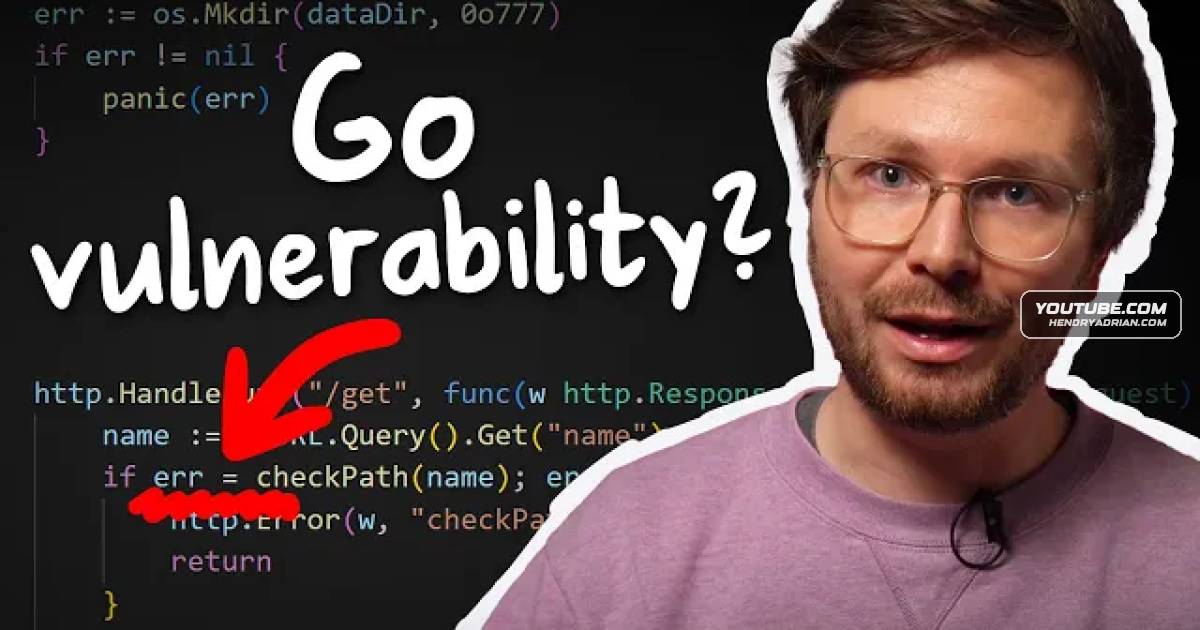
A CTF challenge exposed a Go race condition: concurrent requests could reset a shared error variable and bypass a path check to read the flag file. The video explains the bug and exploit.
Key points
- The challenge’s Go HTTP handlers process requests concurrently and share an error variable because one assignment uses = rather than declaring a new variable.
- The path check sets the shared error when a request targets flag.txt, but another request can reset it to nil before the check completes.
- By repeatedly sending requests to trigger that race, the exploit can bypass the path check and read the flag file.
- The video also describes an unintended route: examining other processes’ file descriptors through /proc could reveal a flag file opened by a challenge health check.
- The challenge used a separate backend process per session, limiting race-condition interference between teams.
Article Details
- Topics
- [00:00] Black-box backend fingerprinting through JSON parser behavior
- [01:32] Go key-value store CTF challenge architecture
- [05:55] Unintended flag disclosure through process file descriptors
- [09:17] Go shared-variable race condition and path-check bypass
- [12:57] Exploit using concurrent requests to read the flag