
Inside Mozilla’s Response to a Firefox Zero-Day at Pwn2Own
· 15:10 · Watch on YouTube ↗
Summary
Pwn2Own researchers demonstrated a Firefox zero-day involving an out-of-bounds write in SpiderMonkey’s Promise.allSettled implementation. Mozilla reproduced the issue and investigated variants before preparing a patch.
Key points
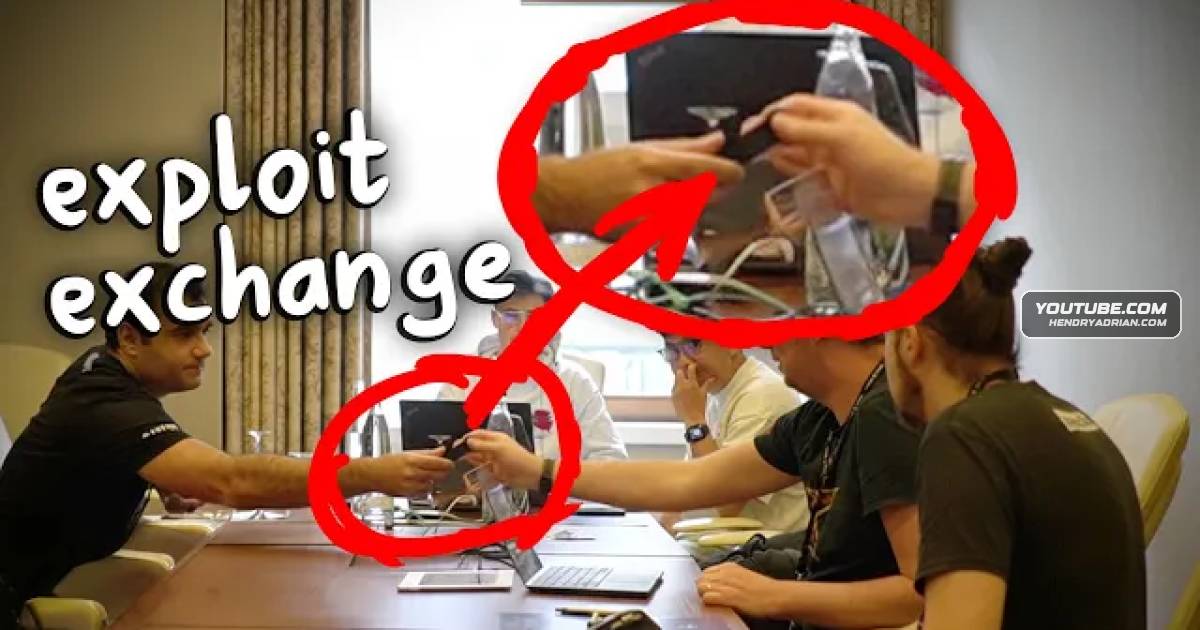
- Researchers Eduardo Bojin and Tawan demonstrated the Firefox exploit at Pwn2Own and shared a proof of concept with Mozilla.
- The bug involves SpiderMonkey’s Promise.allSettled implementation: a mutable index can enable an out-of-bounds read and then bypass a check to perform an out-of-bounds write.
- Mozilla reproduced the issue in debug builds, where an assertion prevents exploitation, and traced it to builds going back to when the API was added.
- Mozilla treated the disclosure as an incident-response exercise, coordinating investigation, engineering, and release work.
- Mozilla had a prototype fix but was checking for related variants before release; the transcript does not report that a patch had shipped.
- The video says Firefox ESR and Tor Browser were affected, and distinguishes this private Pwn2Own finding from a publicly known in-the-wild zero-day.
Article Details
- Topics
- [00:00] Pwn2Own Firefox zero-day demonstration and disclosure process
- [02:34] SpiderMonkey Promise.allSettled vulnerability mechanics
- [04:20] Proof-of-concept reproduction and investigation of the bug’s history
- [05:51] Exploit stability challenges and Firefox exploitation details
- [07:39] Mozilla’s incident coordination and affected Firefox ESR and Tor Browser
- [10:46] Patch development, variant analysis, and release-risk assessment
People
Eduardo BojinPalo Alto Networks researcher who demonstrated a Firefox zero-day exploit at Pwn2Own.FreddyMozilla incident manager who coordinated the response, shared the exploit sample with the team, and helped manage investigation tasks.TawanPalo Alto Networks researcher who demonstrated a Firefox zero-day exploit at Pwn2Own.