
Team Cymru Details Scout and Recon Workflows for Threat Hunting
Summary
Team Cymru describes how its SecOps team uses Scout and Recon to investigate alerts, suspicious emails and malware, hunt for unusual activity involving public IP space, and automate threat-intelligence queries.
Key points
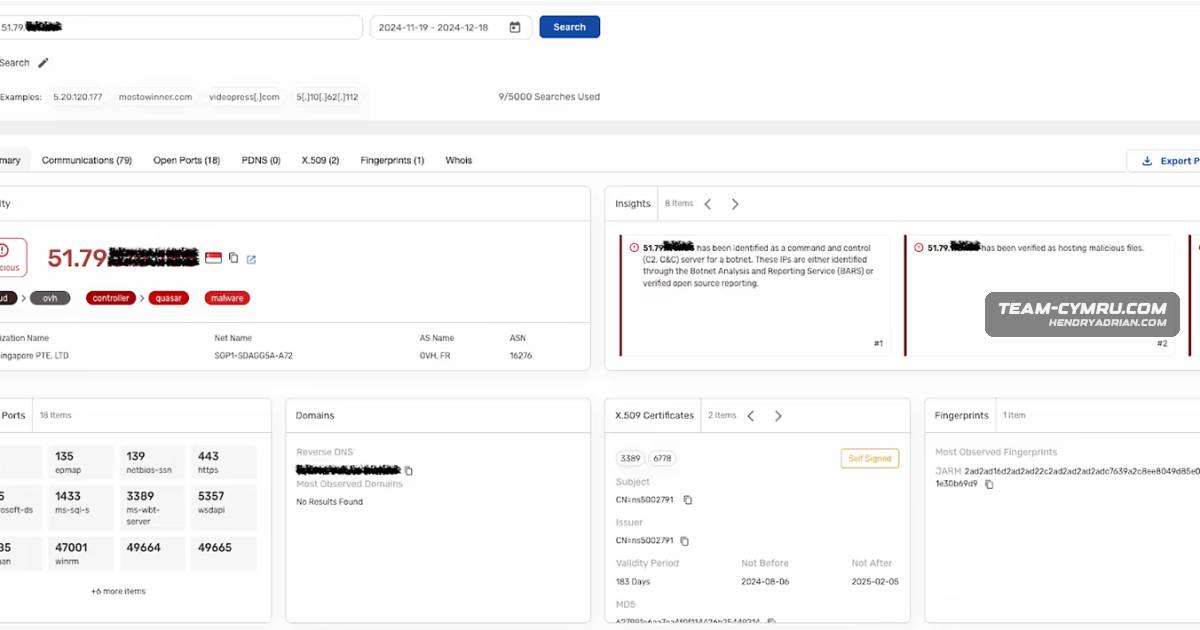
- Scout can provide quick threat context for URLs and public IPs, including an example IP associated with the Quasar malware family.
- For suspicious emails, the team uses Scout to examine URLs, attachments and headers, then pivots to Recon for more detail.
- Scout looks back up to 90 days but limits queries to a 30-day window; Recon can query across its available time window.
- Recon’s malware add-on can sandbox attachments not already present in its malware-sample database.
- The team describes proactive threat reconnaissance using OSINT and searches for unusual activity involving Team Cymru public IP space.
- A Scout query can search for Discord communications involving a CIDR of interest, with results available for more granular investigation in Recon.
- The Scout API can automate recurring workflows, such as finding Offensive Security Tool-tagged IPs communicating with the team’s public IP space.
Article Details
- Defense Focus
- Use threat-intelligence and network-telemetry workflows to triage suspicious emails and attachments, hunt for threats affecting Team Cymru public IP space, and enrich malware analysis.
- Detection Methods
- Search Scout using a URL or public IP for initial threat context, then pivot to Recon for more detailed investigation.
- Review suspicious email URLs, attachments, and headers; use Recon's malware add-on to sandbox attachments.
- Hunt for traffic associated with reported Discord C2 abuse using the Scout filters comms.tag = "discord" and comms.peer = "*CIDR of interest*".
- Use Scout API queries to identify OST-tagged IPs communicating with public IP space, then query those IPs for more information.
- Data Sources
- URLs and public IP addresses
- Suspicious email headers, URLs, and attachments
- Network communication metadata, including comms tags and peer IPs
- Team Cymru public IP space
- Malware samples and malware-analysis data
- Cybersecurity news and OSINT
- Rule Types
- Scout search queries using communication-tag and peer-IP filters
- Scout API searches and IP-detail queries
- Platforms
- SIEMs
- Defensive Actions
- Use Scout for rapid initial triage and Recon when more detailed or longer-window investigation is needed.
- Sandbox suspicious attachments with Recon's malware add-on.
- Automate recurring threat-reconnaissance workflows with the Scout API and review queried IP details or trends.
- Monitor cybersecurity news for indicators and assess potential exposure of the organization and its suppliers.
- Use the Malware Hash Registry to enrich malware-analysis workflows.
MITRE ATT&CK
Malware
Vendors
Products
Tools
Malware Hash RegistryI think a lot of people don’t know about our malware utility, Malware Hash Registry (MHR). It’s a neat way to enhance your malware analysis workflows without the complexity of adding multiple AV scanners. You can readReconScout and Recon are both excellent tools for day-to-day SecOps tasks.scoutAs an amuse bouche, our Scout threat hunting tool is a great place for us to begin. Investigating an alert from your SIEM? Just enter a URL or public IP into the Scout search bar to get started. Here we have some useful