
Abbott Investigates Two Cyber Incidents Amid Extortion Claims
Summary
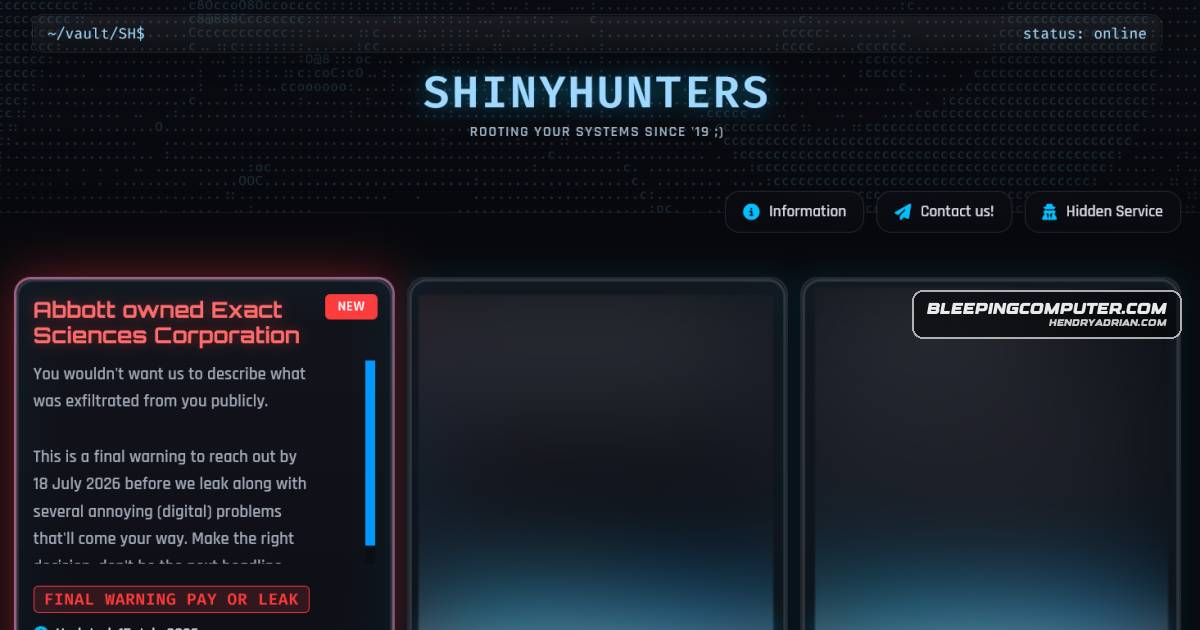
Abbott confirmed unauthorized access to legacy Cancer Diagnostics systems and is investigating a separate LabCentral breach claim. It reports no operational impact and disputes that LabCentral holds sensitive data; the actors’ theft claims remain unverified.
Key points
- Abbott confirmed unauthorized access to a limited number of legacy Exact Sciences systems in its Cancer Diagnostics business; it said other Abbott systems were unaffected.
- Abbott said the Cancer Diagnostics incident did not affect operations, manufacturing, lab work, or patient services. It activated incident response, engaged cybersecurity experts, and notified law enforcement.
- ShinyHunters claimed it used vishing to compromise a Microsoft Entra SSO account and steal internal documents and large amounts of personal and medical data; BleepingComputer could not independently verify the claims.
- A second actor, ShadowByt3$, claimed it accessed Abbott’s LabCentral portal using compromised customer credentials and exfiltrated files through API endpoints.
- Abbott acknowledged a potential LabCentral incident but disputed the claim that the portal contained sensitive data, saying it holds publicly available technical documents.
- Neither actor had publicly released the data they claimed to have stolen at the time of reporting.
Article Details
- Victim Organization
- Abbott Laboratories
- Incident Type
- Two separate incidents: Abbott confirmed unauthorized access to a limited number of legacy internal systems in its Cancer Diagnostics business. Separately, ShadowByt3$ claimed it breached the LabCentral portal using compromised customer credentials and exfiltrated files through API endpoints; Abbott described this as a potential incident and disputed that the data was sensitive.
- Incident Date
- 2026-07-04
- Data Types Exposed
- ShinyHunters claimed to have stolen internal documents, contracts, customer information, personally identifiable information, Social Security numbers, client notes containing doctor-patient conversations, medical orders, customer agreements, and NDAs; these claims have not been independently verified.
- ShadowByt3$ claimed to have obtained technical and business documents, including manufacturing certificates, operating manuals, technical specifications, regulatory documentation, product requirement archives, calibrator value assignments, and assay files. Abbott said LabCentral contains publicly available technical documents and no sensitive customer or business information.
- Affected Records
- ShinyHunters claimed more than 30 million rows of customer PII, including over one million Social Security numbers, more than 22 million client notes, and more than 20 million medical orders. These figures were not independently verified.
- Operational Impact
- Abbott said the Cancer Diagnostics incident did not affect business operations, product availability, manufacturing, lab operations, or patient services, and did not affect other Abbott businesses or systems. Abbott did not expect a material impact on its business or financial results.
- Ransom Or Extortion
- ShinyHunters added Abbott to its leak site and threatened to publish allegedly stolen data unless Abbott negotiated, initially setting a deadline after July 18 and later extending it to July 21. Neither group had publicly released the data it claimed to have stolen at the time of the report.
- Claim Status
- alleged
MITRE ATT&CK
Threat Actors
ShadowByt3$Claimed to have breached Abbott's LabCentral portal using compromised customer credentials and to have exfiltrated files by targeting API endpoints. Abbott described the incident as potential and disputed the claim that the stored data was sensitive.ShinyHuntersClaimed it used vishing to compromise an employee's Microsoft Entra SSO account, access internal systems, and steal data from connected services. It also threatened to publish allegedly stolen data. The reported data theft claims were not independently verified.
Products
CoupaWhen asked what data was allegedly stolen, ShinyHunters claimed it exfiltrated data from Microsoft Entra, ServiceNow, SharePoint, Databricks, and Coupa, including internal documents, contracts, and customer information.DatabricksWhen asked what data was allegedly stolen, ShinyHunters claimed it exfiltrated data from Microsoft Entra, ServiceNow, SharePoint, Databricks, and Coupa, including internal documents, contracts, and customer information.LabCentralAbbott Laboratories is investigating two separate cybersecurity incidents involving its Cancer Diagnostics business and its LabCentral portal, with one linked to ShinyHunters and the other to ShadowByt3$.Microsoft EntraAccording to the threat actor, the attack allowed it to compromise a Microsoft Entra single sign-on (SSO) account and gain access to internal systems.Microsoft SharePointWhen asked what data was allegedly stolen, ShinyHunters claimed it exfiltrated data from Microsoft Entra, ServiceNow, SharePoint, Databricks, and Coupa, including internal documents, contracts, and customer information.ServiceNowWhen asked what data was allegedly stolen, ShinyHunters claimed it exfiltrated data from Microsoft Entra, ServiceNow, SharePoint, Databricks, and Coupa, including internal documents, contracts, and customer information.