
DNS Analysis Identifies Additional Infrastructure Linked to RatHat Android Malware
Summary
A DNS and WHOIS investigation into RatHat, an Android malware campaign spread via smishing and malvertising, identified 33 network IoCs, 240 communicating client IPs, and additional potentially malicious domains.
Key points
- Zimperium reported that RatHat spreads through targeted smishing and malvertising, and uses Accessibility abuse and local ADB self-pairing to run native daemons with shell-level privileges.
- The investigators assembled 33 network IoCs: 15 subdomains and 18 domains, after identifying a likely legitimate domain among the candidates.
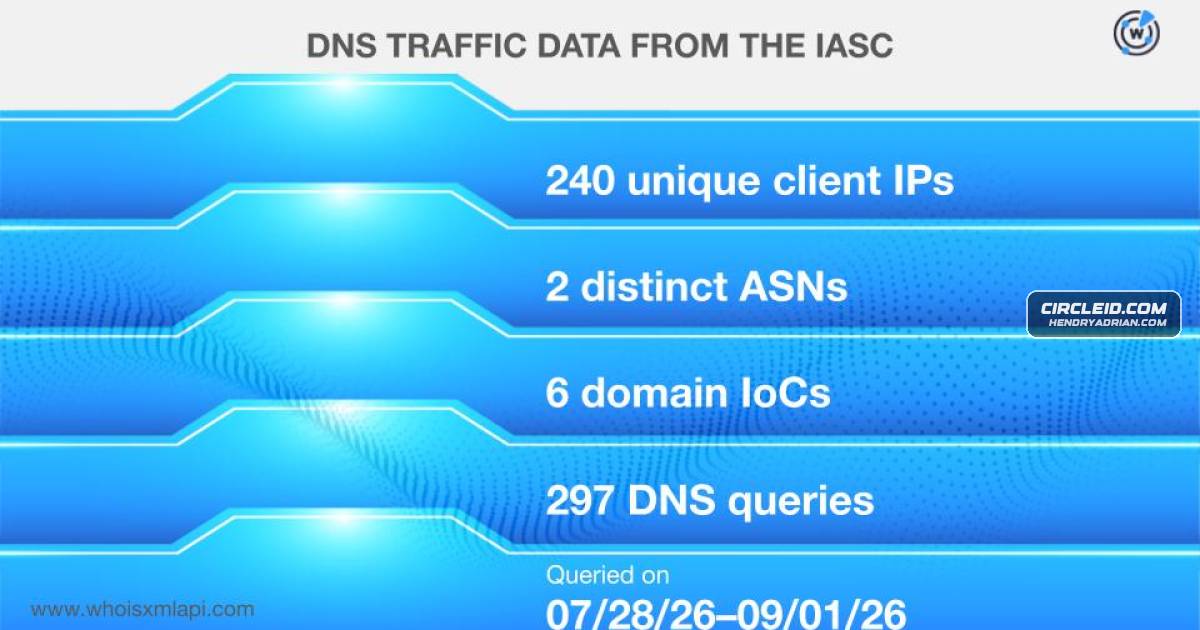
- They observed 240 client IP addresses across two ASNs making 297 DNS queries to six IoC domains between July 28 and September 1, 2026.
- Three IoC domains appeared in two typosquatting groups containing five to six members each.
- Historical WHOIS and reverse-WHOIS analysis linked eight public email addresses to 8,461 domains; four were flagged as weaponized, including qfdhb[.]com.
- The researchers also reported seven malicious IP addresses and three IP-connected domains, one of which was flagged as malicious. They cautioned that some threat classifications may change with further investigation.
Article Details
- Attack Vectors
- Targeted smishing and malvertising led victims to deceptive third-party download portals.
- After deployment, RatHat abused Android Accessibility features and used autonomous local ADB self-pairing to escape the standard application sandbox.
- RatHat staged independent native daemons that executed with shell-level privileges.
- The malware used generative AI for operational control.
- Defensive Notes
- The article cautions that entities identified as malicious may later be deemed harmless and recommends supplementary investigation to corroborate findings.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | gpgmk[.]com | RatHat domain IOC that the article says appeared in a malicious-domains feed before being tagged as an IOC. |
| DOMAIN | kingbss[.]com | Listed as a RatHat domain IOC in the article's DNS-history analysis. |
| DOMAIN | primevoria[.]com | Listed as a RatHat domain IOC in the article's DNS-history analysis. |
| DOMAIN | qfdhb[.]com | Email-connected domain the article says has been associated with malware distribution since 9 March 2023. |
| DOMAIN | uuokxx[.]com | Listed as a RatHat domain IOC in the article's DNS-history analysis. |
| DOMAIN | xiogmaocs[.]mom | Lookalike domain in a typosquatting group registered alongside the RatHat IOC xiongmaocs[.]help. |
| DOMAIN | xiongmaocs[.]best | Lookalike domain in a typosquatting group registered alongside the RatHat IOC xiongmaocs[.]help. |
| DOMAIN | xiongmaocs[.]help | RatHat domain IOC described as bulk-registered alongside lookalike domains. |
| DOMAIN | xiongmaocs[.]mom | Listed as a RatHat domain IOC in the article's DNS-history analysis. |
| DOMAIN | xiongmaoll[.]xyz | Lookalike domain in a typosquatting group registered alongside the RatHat IOC xiongmaocs[.]help. |
| DOMAIN | xiongmaoys[.]help | Lookalike domain in a typosquatting group registered alongside the RatHat IOC xiongmaocs[.]help. |
| HOSTNAME | admin[.]fjbjwgyuyftg[.]qpon | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | admin[.]niaotong2[.]top | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | admin[.]xiongmaocs[.]help | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | admin[.]xiongmaocs[.]mom | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | admin[.]xiongmaocs[.]pics | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | bc[.]etlva[.]cn | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | cunzhang[.]krgdef[.]cn | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | cz[.]gpgmk[.]com | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | fegrs[.]adidasabc[.]com | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | jiaozhu[.]etlva[.]cn | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | mao[.]terh5[.]cn | Subdomain IOC flagged as malicious by the Threat Intelligence API. |
| HOSTNAME | oop[.]uuokxx[.]com | Subdomain IOC flagged as malicious by the Threat Intelligence API. |