Password-Spraying Campaign Targets AWS Root Accounts at 150+ Organizations
Summary
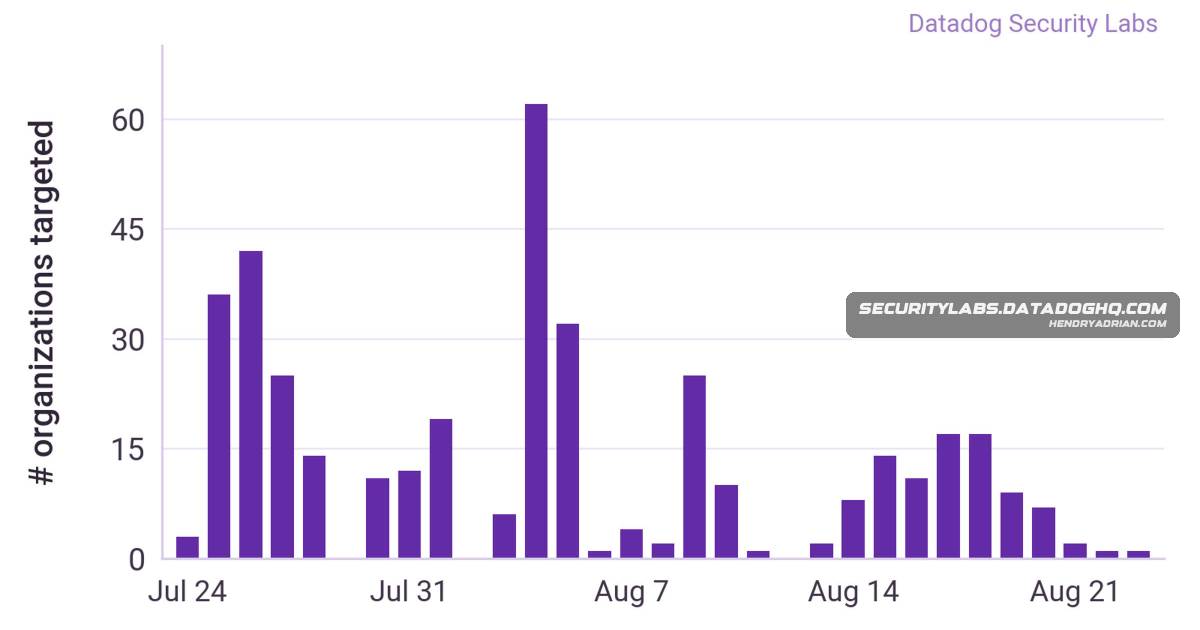
Datadog observed failed AWS root-account login attempts at more than 150 organizations from July 24 to August 23, 2026. No successful logins were observed, and the attacker’s intent remains unknown.
Key points
- The campaign generated repeated failed AWS root-user authentication attempts; organizations saw a median of two attempts, with some seeing up to eight.
- Datadog identified two Chrome and Firefox user-agent strings and requests routed through proxy infrastructure spanning many countries and ASNs.
- A failed root ConsoleLogin requires the account’s associated email address, suggesting attackers had an email list or tested addresses to find valid accounts.
- Datadog observed no successful authentication and could not determine the attacker’s motive.
- Organizations can search CloudTrail for root ConsoleLogin events, including failures, using the reported user-agent fingerprints.
- AWS root activity should be monitored; recommendations include reducing persistent root credentials, using centralized root access and short-lived sessions, and alerting on root activity.
Article Details
- Event Type
- Password-spraying campaign targeting AWS root user accounts
- Impact
- Attackers made repeated failed authentication attempts against root accounts at more than 150 organizations between 2026-07-24 and 2026-08-23. Datadog reported no observed successful authentication and could not determine the campaign's intent.
MITRE ATT&CK
Vendors
Products
AWS OrganizationsAWS Organizations service control policies can prevent direct root activity in member accounts.Cloud SIEMCloud SIEM:CloudTrailOrganizations should also treat all root activity as security-relevant, and alert on direct root sign-ins, root API activity, credential changes, and centrally initiated privileged sessions recorded in CloudTrail.