Placeholder domain used in dev docs now serves ClickFix attacks
Summary
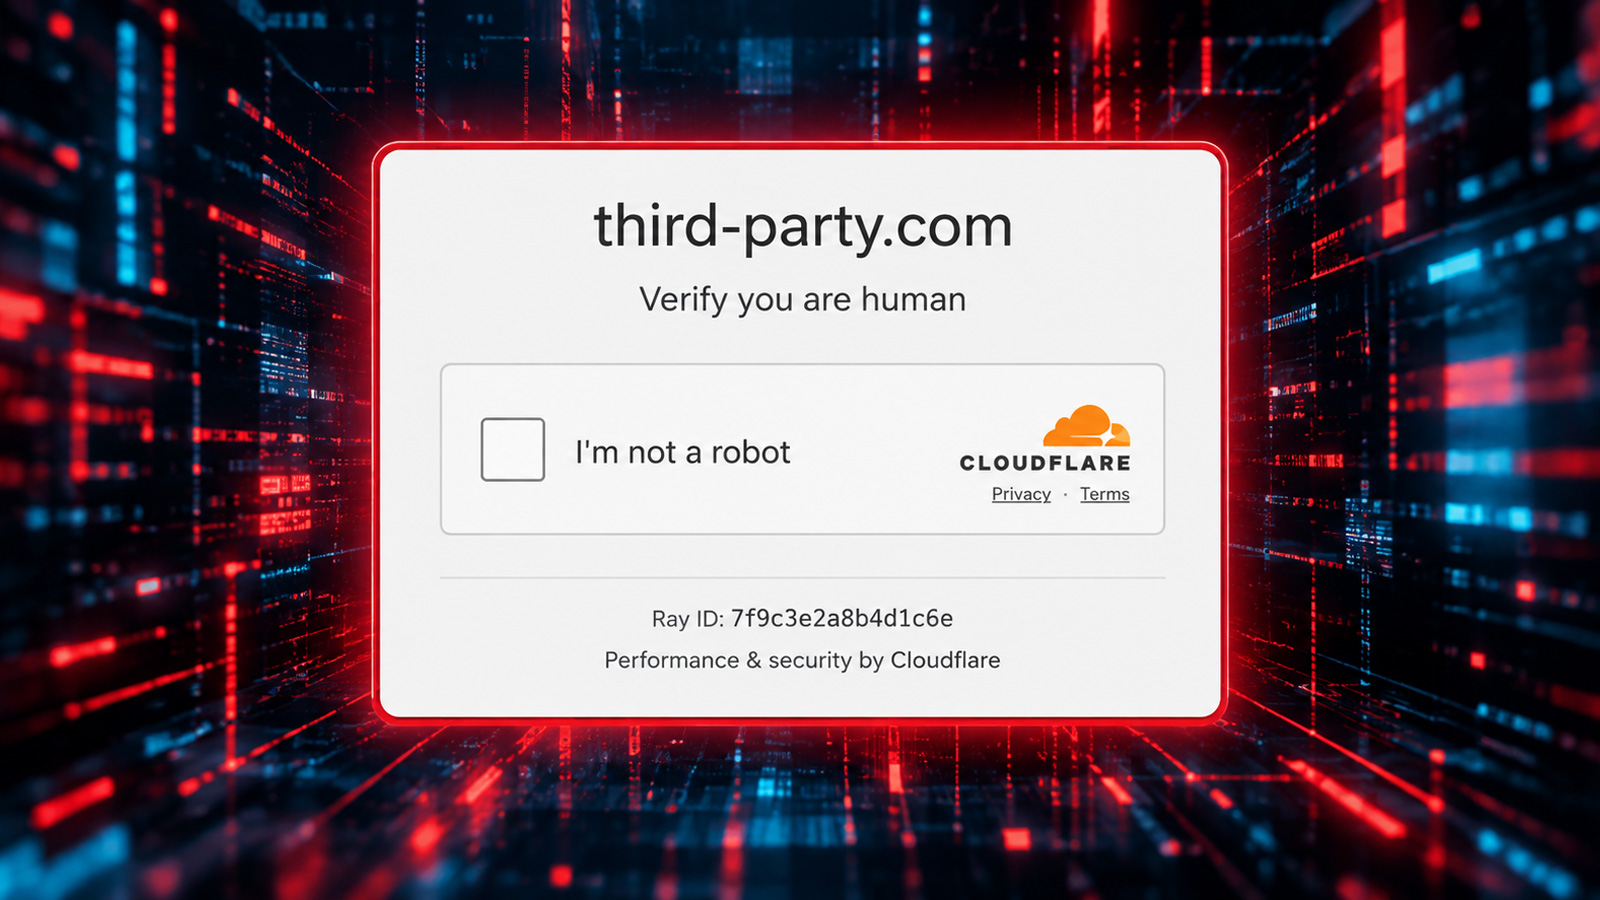
The normally registered third-party.com domain is serving a fake Cloudflare verification page that uses a ClickFix technique to trick Windows users into running a PowerShell command. The command downloads and executes a script from elxxvvx[.]xyz. The payload domain no longer resolved during BleepingComputer's testing, and the archive previously distributed from it is unavailable.
Key points
- The fake verification page copies a PowerShell command to the Windows Clipboard and instructs users to run it through the Windows Run dialog.
- The command reconstructs a payload URL at elxxvvx[.]xyz/f, downloads a PowerShell script, and executes it.
- A Hybrid Analysis report dated May 2, 2026, showed the script downloading a 134MB archive from https://elxxvvx[.]xyz/update2.zip, extracting it, and attempting to launch draw.io.exe.
- The archive is no longer available, so BleepingComputer could not determine what the payload does.
- Manifold Security reported the malicious use of third-party.com; BleepingComputer confirmed the fake verification page.
- The domain is live, but the payload domain no longer resolved during testing. There have been no reports that the documented references led to successful ClickFix execution.
Tags
ClickFixSocial EngineeringMalicious DomainPowerShellMalware Delivery
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | elxxvvx[.]xyz | Payload domain used by the PowerShell command; it no longer resolved during BleepingComputer's testing. |
| DOMAIN | third-party[.]com | Domain serving the fake Cloudflare verification page used in the ClickFix attack. |
| URL | hxxps[:]//elxxvvx[.]xyz/update2[.]zip | URL from which the script was reported to download a 134MB archive. |